You signed in with another tab or window. Reload to refresh your session.You signed out in another tab or window. Reload to refresh your session.You switched accounts on another tab or window. Reload to refresh your session.Dismiss alert
{{ message }}
Repository navigation
limit accepted message passwords based on password policy #1618
changed the title [-]limit accepted passwords based on password policy - will share[/-][+]limit accepted message passwords based on password policy - will share[/+]on Dec 20, 2021
We'll need a method that will validate user message passwords to make sure it complies with password policy. I'll share the policy separately (not public).
The implementation can check for all of these rules at once and when not conforming, show:
Password didn't comply with company policy, which requires at least:

 - one uppercase
 - one lowercase
 - one number
 - one special character eg &"#-'_%-@,;:!*()
 - 8 characters length

Please update the password and re-send.
changed the title [-]limit accepted message passwords based on password policy - will share[/-][+]limit accepted message passwords based on password policy[/+]on Jan 13, 2022


Activity
[-]limit accepted passwords based on password policy - will share[/-][+]limit accepted message passwords based on password policy - will share[/+]tomholub commentedon Dec 20, 2021
We'll need a method that will validate user message passwords to make sure it complies with password policy. I'll share the policy separately (not public).
DenBond7 commentedon Jan 6, 2022
@tomholub Any news here?
tomholub commentedon Jan 6, 2022
Sorry, it's stuck on me.
DenBond7 commentedon Jan 6, 2022
Don't worry. I'm going to work on #1620
tomholub commentedon Jan 13, 2022
when using FES to send the password protected message, use the following password rules:
&"#-'_-@,;!*()[]etctomholub commentedon Jan 13, 2022
The implementation can check for all of these rules at once and when not conforming, show:
[-]limit accepted message passwords based on password policy - will share[/-][+]limit accepted message passwords based on password policy[/+]11 remaining items
DenBond7 commentedon Jan 22, 2022
@tomholub Looks better?
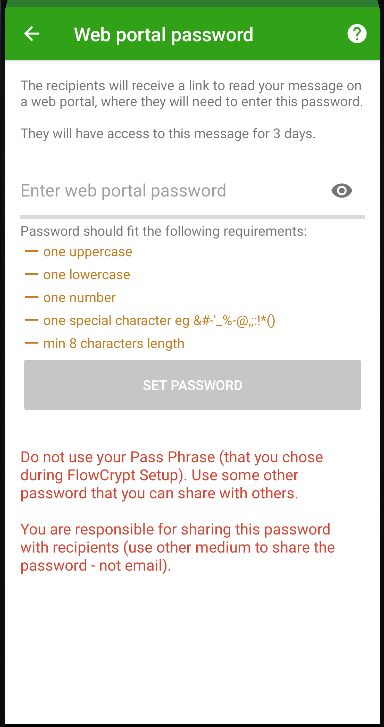
Modified UI. Added some logic.| #1618
tomholub commentedon Jan 22, 2022
Sure. Less pretty but also less confusing :-)
Two things I noticed:
They will have access to this message for 180 days.DenBond7 commentedon Jan 22, 2022
tomholub commentedon Jan 22, 2022
yup
Added a few minor changes.| #1618
Fixed existing tests.| #1618
IvanPizhenko commentedon Jan 22, 2022
put "min 8 characters" on top of the list
DenBond7 commentedon Jan 22, 2022
tests
message type == standardMoved "min 8 characters" on top of the list.| #1618
Modified CreateMessageFragmentPasswordProtectedTest. Added ProvidePas…
Refactored code.| #1618
Refactored code. Step 2.| #1618
Issue 1618 limit accepted message passwords based on password policy (#…